
Critical PHP Vulnerabilities (CVE-2026-109618 & CVE-2026-109619): Our Proactive Security Response
 Olivia H.2 min read
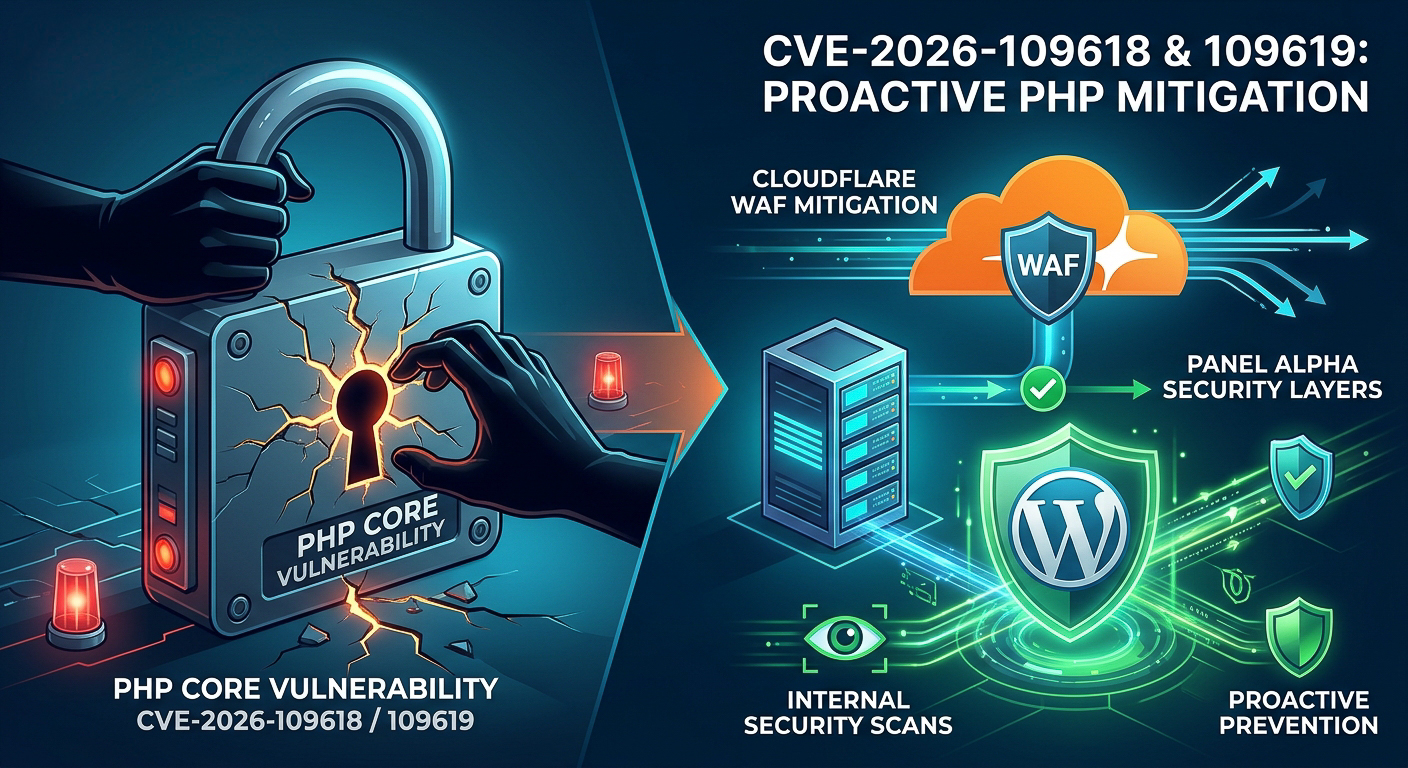
Security in managed WordPress hosting is not just about reacting to threats as they happen-it is about maintaining a rigorous, multi-layered defense architecture before issues ever impact production environments.
Recently, the security community disclosed two critical vulnerabilities in the PHP runtime itself, tracked as CVE-2026-109618 and CVE-2026-109619 (often discussed across the ecosystem as php2shell). Rated with a severe CVSS score of 9.2 / 10, these memory-handling flaws can potentially allow unauthenticated remote code execution or data exposure if left unmitigated.
Because these flaws reside deep within the PHP interpreter rather than in individual WordPress plugins or themes, addressing them requires a coordinated, infrastructure-wide response. Here is how OneStopWP protects your websites against these emerging threats.
1. Understanding the Vulnerabilities (CVE-2026-109618 & CVE-2026-109619)
The core of the issue involves how PHP handles memory allocation and error cleanup during abnormal HTTP request interruptions:
- CVE-2026-109618: Out-of-memory handling leaves internal PHP request data in an uninitialized or invalid state during cleanup, which can lead to unsafe memory execution.
- CVE-2026-109619: A fatal error interrupts a request while PHP holds references to memory slated for release. Subsequent requests in the same process can access these outdated references, exposing sensitive data.
Because PHP underpins nearly 70% of the web-including mission-critical WordPress sites-proactive edge and server-side filtering are mandatory.
2. Multi-Layered Defense: How OneStopWP Keeps You Safe
At OneStopWP, your sites do not rely solely on reactive patching. We maintain a robust defense-in-depth strategy:
A. Edge-Level Protection via Cloudflare DNS & WAF
As a core part of our infrastructure stack, we leverage Cloudflare as our DNS and security edge. Cloudflare proactively deployed advanced Web Application Firewall (WAF) rules-including full transaction detection combining request and response signals-ahead of public disclosure to intercept exploit attempts at the network edge. This ensures that malicious payloads targeting these memory flaws are blocked before they ever reach your origin server.
B. Infrastructure Hardening via PanelAlpha
For our control panel and container orchestration, we rely on PanelAlpha. Following the disclosure, the PanelAlpha team rapidly released critical updates (such as PanelAlpha v1.9.8.3 and Engine updates) incorporating the official PHP security backports (8.2.35, 8.3.36, 8.4.27, and 8.5.12). Our engineering team immediately integrated these patches across our managed server nodes.
C. Continuous Internal Security Audits & Proactive Scans
Beyond perimeter defenses and automated updates, OneStopWP performs rigorous internal security scans across all containerized environments, cron jobs, and database endpoints. By continuously auditing execution states and tracking anomalous resource utilization, our systems catch and neutralize potential risks proactively.
Your Peace of Mind is Our Priority
Managed WordPress hosting means you never have to scramble when zero-day or high-severity vulnerabilities hit the news cycle. While our automated WAF rules and updated PHP runtimes have your infrastructure covered, our team continues to monitor threat feeds around the clock.
👉 Experience secure, high-performance hosting built for modern standards. Explore OneStopWP managed plans today.
See our plans and grab your discount while promotions last.
See plansKeep reading
All posts → WordPress Hosting & OptimizationPHP 8.3 and Beyond: Why Your Host’s PHP Version Dictates Site SpeedOlivia H.Date: Jun 23, 2026
 WordPress Hosting & OptimizationMastering WP AI Connectors: The Future of Native WordPress IntelligenceDenny G.Date: Jun 2, 2026
 WordPress Hosting & OptimizationWordPress 7.0 Is Here: AI Core, DataViews, and What It Means for YouDenny G.Date: May 20, 2026
Stay up to date
Get WordPress hosting tips, product updates and resources straight to your inbox.