
From 7.0 to 7.1.5: A Roundup of WordPress Core Maintenance and Minor Releases
 Olivia H.4 min read
Major WordPress milestones like 7.0 and 7.1 grab all the headlines with AI connectors, DataViews enhancements, and block editor upgrades. In production hosting environments, however, long-term site stability and security depend just as heavily on the point releases that follow.
With the urgent release of WordPress 7.1.5 on November 18, 2026-a major security update addressing 18 distinct vulnerabilities and 2 core hardening improvements-the 7.x branch has reached a critical security checkpoint ahead of WordPress 7.2 (scheduled for December 8, 2026).
Here is a breakdown of why minor releases matter, what was patched in WordPress 7.1.5, and how managed infrastructure keeps your sites protected without manual intervention.
1. Why Point Releases (7.0.x – 7.1.x) Are Critical for Production Sites
While major releases introduce new capabilities, minor releases (x.x.1, x.x.2, etc.) focus strictly on bug fixes, performance regressions, and security patches. Skipping or delaying point releases leaves high-traffic websites exposed to publicly disclosed attack vectors-especially since core changelogs immediately reveal vulnerable code paths to automated scanners.
Across the 7.0.x and 7.1.x cycle, core maintenance updates have focused on three primary pillars:
- Cryptographic & Transport Hardening: Beginning in WordPress 7.0 and backported down to legacy branches in this latest cycle, legacy 1024-bit root certificates were stripped from WordPress's bundled certificate store to enforce modern TLS standards.
- Block Editor & REST API Stability: Refinements to block serialization, DataViews queries, and REST endpoint permission checks prevent malformed requests from degrading database performance.
- Zero-Day Vulnerability Mitigation: Rapid short-cycle security patches close privilege escalation and injection flaws before widespread exploitation occurs.
2. Inside WordPress 7.1.5: Key Security Patches & Hardening
WordPress 7.1.5 is a mandatory security release. Security researchers and the WordPress Security Team resolved 20 total security items (18 vulnerabilities plus 2 defensive hardening changes), with backports also issued for legacy branches all the way back to WordPress 4.7 (such as 7.0.9 and 6.9.12).
Critical Highlights Site Owners Should Know:
- Unauthenticated Privilege Escalation & RCE Risk: A high-severity flaw in Template Part block attributes could allow unauthenticated attackers to escalate privileges and potentially achieve Remote Code Execution (RCE).
- Multisite Admin-to-Super-Admin Escalation: A cross-context validation flaw in Customizer navigation-menu previews allowed a standard Multisite Administrator to escalate to Super Administrator privileges.
- Two SQL Injection Flaws: Core developers patched SQL injection vectors in nested
WP_Meta_Queryrelation values as well as front-page settings inside Customizer changeset previews. - Multiple Stored Cross-Site Scripting (XSS) Bugs: Patches address unauthenticated stored XSS via shortcode attributes in comments, alongside block editor XSS vectors involving Openverse image metadata and media-to-File block conversions.
- XML-RPC Denial of Service (DoS): Unauthenticated clients could previously batch multiple
pingback.pingcalls inside a singlexmlrpc.phpsystem.multicallrequest to amplify CPU and MySQL load. - Information Disclosure & Authorization Bypasses: Fixes prevent unauthorized exposure of private taxonomy terms via the REST search endpoint, user email addresses in REST comment responses, and unpublished Customizer changesets.
3. Post-Update Verification Checklist
Even when automatic background updates are enabled, relying on "set and forget" maintenance can leave sites vulnerable if a file permission lock or transient timeout interrupts the upgrade. After updating to 7.1.5, verify the following:
- Confirm Core Version: Check Dashboard → Updates (or run
wp core versionvia WP-CLI) to ensure your instance reports7.1.5(or7.0.9if pinned to the 7.0 branch). - Flush Object & Page Caches: Clear your full-page cache and persistent Redis object cache so stale admin scripts or REST responses are purged cleanly.
- Audit User Roles: Because several patched XSS and authorization flaws required Contributor or Author access, review your Users list and remove dormant accounts.
Proactive Core Management & Edge Defense at OneStopWP
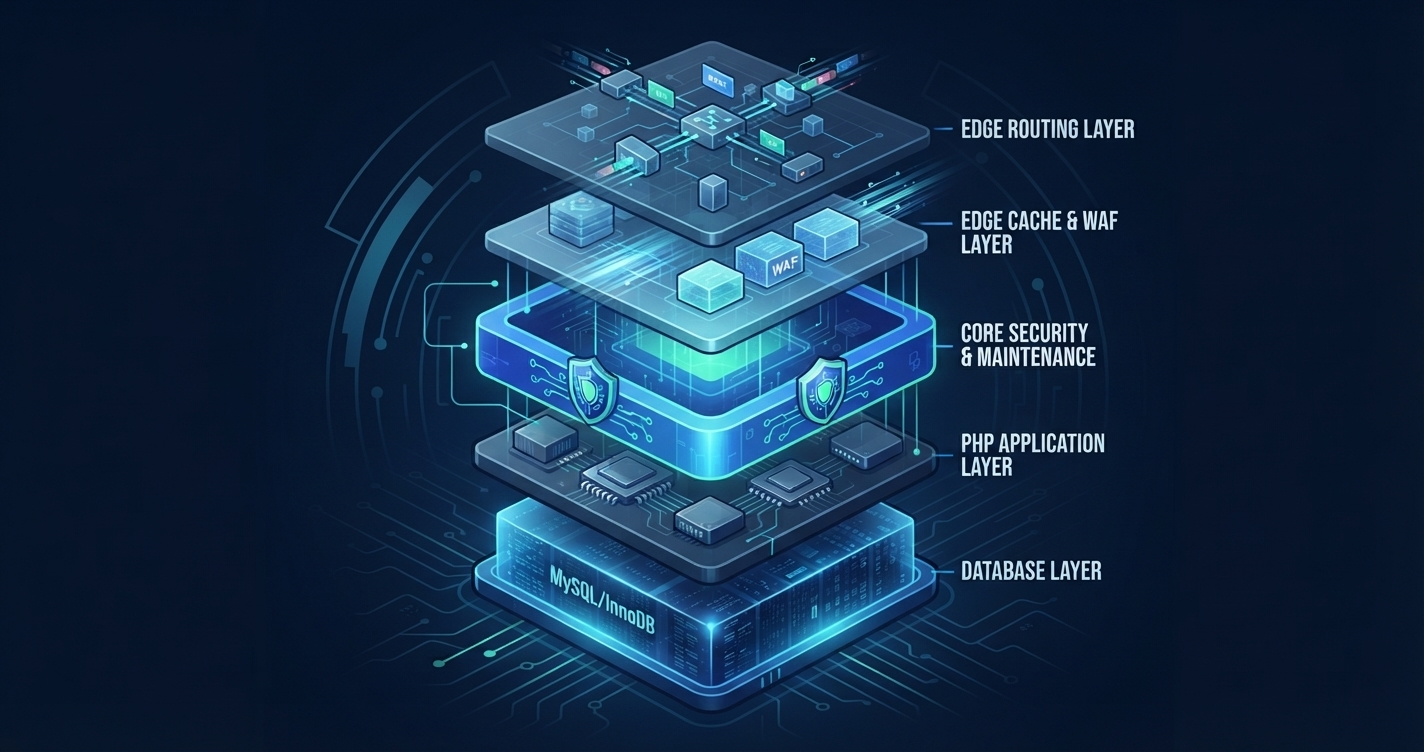
At OneStopWP, core security updates are treated as an infrastructure priority rather than an afterthought. Powered by modern orchestration and our multi-layered defense stack, your WordPress instances benefit from:
- Automated Core Security Rollouts: Managed minor updates and verified backups ensure your sites receive critical patches like 7.1.5 rapidly without manual guesswork.
- Built-In Security Audits with OneStopWP Optimizer: Included with every OneStopWP hosted site, OneStopWP Optimizer brings security health checks onto a single screen inside your WordPress dashboard-letting you verify core/PHP hardening and apply common security fixes with a single click.
- Cloudflare Edge WAF Protection: Even before core patches are applied, our edge-level Web Application Firewall filters malicious SQL injection payloads, XSS attempts, and abusive
xmlrpc.phpmulticall floods before they ever reach your origin container. - Clean Cache Invalidation with WPCacheOn: Pair core updates with our WPCacheOn plugin (also available on WordPress.org) to purge page caches and Redis Object Cache keys cleanly after every release.
👉 Want worry-free WordPress core updates and edge-level security? Explore OneStopWP Managed Hosting plans today.
See our plans and grab your discount while promotions last.
See plansKeep reading
All posts → WordPress Hosting & OptimizationOneStopWP Optimizer: Free Security Checks and One-Click Fixes for Every OneStopWP Hosted SiteDenny G.Date: Nov 9, 2026
 WordPress Hosting & OptimizationCritical PHP Vulnerabilities (CVE-2026-109618 & CVE-2026-109619): Our Proactive Security ResponseOlivia H.Date: Oct 21, 2026
 WordPress Hosting & OptimizationGlobal Edge Delivery: How CDNs and Server Locations Impact International AudiencesOlivia H.Date: Sep 7, 2026
Stay up to date
Get WordPress hosting tips, product updates and resources straight to your inbox.