
How Automated Botnets Target WordPress (And How Edge-Level WAF Stops Them)
 Olivia H.4 min read
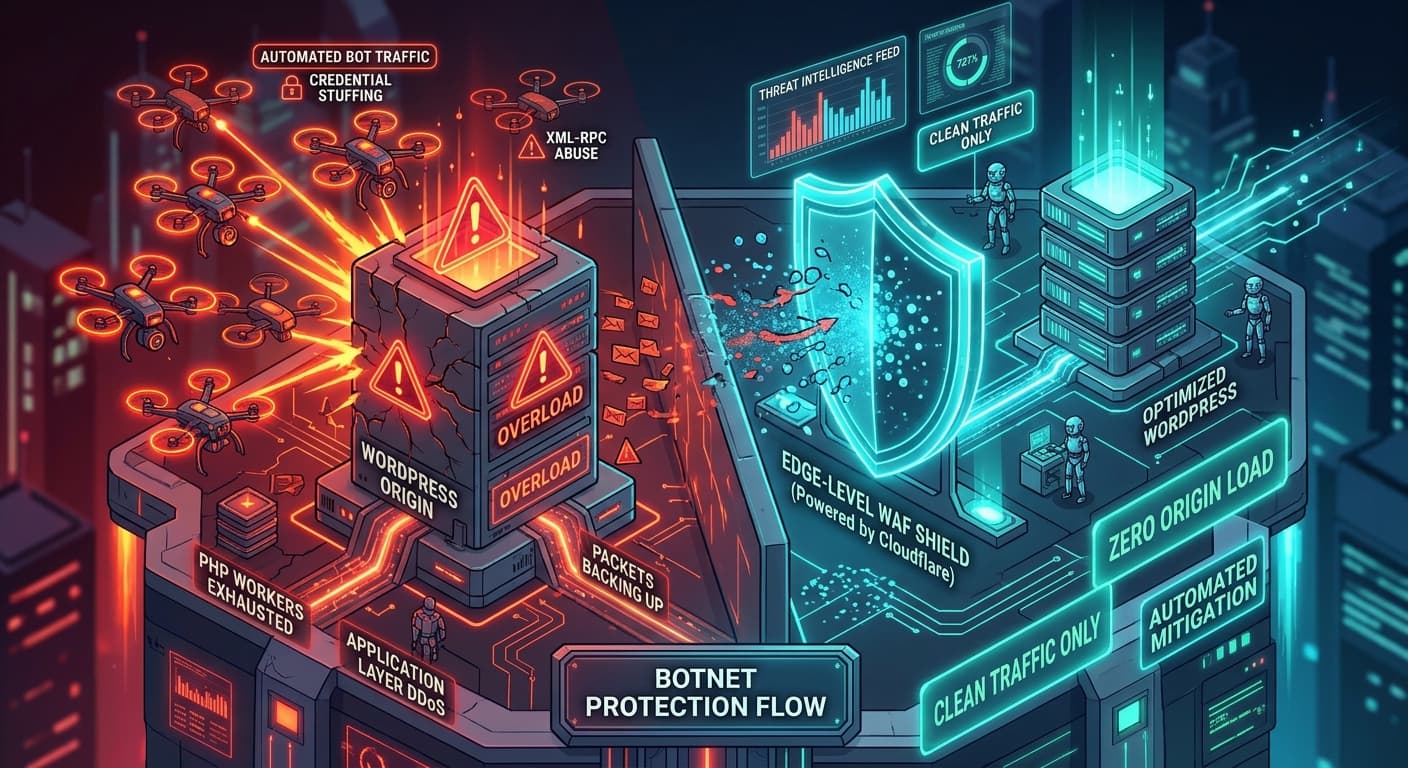
Every single day, millions of automated bots scan the public internet searching for vulnerable WordPress sites. Contrary to popular belief, these attacks are rarely executed manually by targeted hackers; they are orchestrated by distributed botnets-networks of compromised devices executing script-driven attack vectors at massive scale.
When an automated botnet targets your website, the threat isn't just a potential security breach-it’s severe performance degradation. Thousands of malicious HTTP requests hitting your application layer can max out server CPU, exhaust PHP worker pools, and bring down your database.
Let's dissect the primary ways botnets attack WordPress, examine why traditional security plugins struggle to stop them, and explore how edge-level WAF protection solves the problem before malicious traffic ever reaches your server.
1. The Anatomy of a WordPress Botnet Attack
Botnets target specific known entry points in WordPress core and common plugin architectures to compromise credentials or overload infrastructure.
+--------------------------------------------------------------------+
|                   PRIMARY BOTNET ATTACK VECTORS                    |
+--------------------------------------------------------------------+
|  1. Credential Stuffing  --> Automated login attempts using leaked |
|                              username/password databases.          |
|                                                                    |
|  2. XML-RPC Abuse        --> Amplified multi-pass brute-force via  |
|                              the legacy xmlrpc.php endpoint.       |
|                                                                    |
|  3. Application Layer    --> Rapid HTTP GET/POST floods targeting  |
|     DDoS Floods              uncached dynamic endpoints.           |
+--------------------------------------------------------------------+
A. Credential Stuffing & Brute-Force Attacks
Botnets distribute thousands of login requests per minute across wp-login.php. By rotating IP addresses across thousands of compromised IoT devices or residential proxies, they bypass basic single-IP rate limits while attempting millions of common credential combinations.
B. XML-RPC Amplification Attacks
The legacy xmlrpc.php file in WordPress includes a method called system.multicall. This feature allows a client to attempt dozens of authentication guesses within a single HTTP request. A botnet sending 1,000 requests to xmlrpc.php can test 50,000 password combinations, swamping PHP and MySQL instantly.
C. Layer 7 (Application) Resource Exhaustion
Even if a botnet fails to breach your admin credentials, high-frequency automated scraping of search endpoints (/?s=keyword), WooCommerce checkout paths, or dynamic filters forces your server to run expensive, un-cached database queries-leading to 504 Gateway Timeouts for legitimate users.
2. Why Application-Level Security Plugins Fail at Scale
Many site owners rely on popular security plugins to block attacks. While plugins provide useful auditing tools, relying on PHP-level security to stop botnets presents a fundamental architectural flaw: Execution Location.
[ Incoming Botnet Attack ]
           │
           ▼
┌─────────────────────────┐
│     Web Server (Nginx)  │  <-- Server resources consumed
└──────────┬──────────────┘
           │
           ▼
┌─────────────────────────┐
│     PHP Engine (FPM)    │  <-- PHP Worker process spawned
└──────────┬──────────────┘
           │
           ▼
┌─────────────────────────┐
│  Security Plugin Logic  │  <-- Query runs, checks IP, blocks request
└─────────────────────────┘
When a security plugin blocks a botnet request:
- The request reaches your network interface.
- Nginx or Apache accepts the socket connection.
- A PHP worker process is spawned, allocating server memory.
- WordPress initializes, loads core files, and loads the database.
- The security plugin executes its ruleset and rejects the connection.
If a botnet sends 500 requests per second, your server will exhaust its available PHP workers and RAM attempting to process the block rules. Your server still crashes even though the plugin "blocked" the attacks.
3. Stopping Threats at the Perimeter: Edge-Level WAF
The modern solution for robust WordPress botnet protection is migrating threat mitigation from the application layer to the Network Edge.
By utilizing an Edge Web Application Firewall (WAF) powered by global networks like Cloudflare, incoming traffic is analyzed at edge nodes distributed globally before ever reaching your origin server.
[ Incoming Botnet Attack ]
           │
           ▼
┌─────────────────────────┐
│    EDGE WAF SHIELD      │  <-- Attack blocked at the edge in 0ms!
│  (Cloudflare Network)   │      (Zero load on origin server)
└──────────┬──────────────┘
           │ (Clean Traffic Only)
           ▼
┌─────────────────────────┐
│  Your WordPress Origin  │  <-- CPU & RAM remain 100% healthy
└─────────────────────────┘
Key Advantages of Edge Mitigation:
- Zero Origin Load: Malicious requests are dropped at the CDN edge node, consuming zero CPU, RAM, or PHP workers on your hosting server.
- Global Behavioral Intelligence: Edge WAFs analyze threat signals across millions of domains simultaneously, automatically flagging and challenging suspicious bot IPs before they reach your site.
- JS Challenges & Managed Rulesets: Automated bots that cannot execute JavaScript or solve managed challenges are stopped silently at the perimeter.
Enterprise Edge Security with OneStopWP
At OneStopWP, we don't rely on bloated security plugins that slow down your website. Built on isolated containerized nodes and integrated with enterprise Cloudflare Edge WAF and modern architecture, our managed hosting delivers:
- Edge-Level Bot Protection: Automated mitigation of credential stuffing, brute-force, and XML-RPC attacks before they hit your origin.
- Server-Level Optimization: Deep-level PHP and database tuning paired with our own WPCacheOn plugin (available on WordPress.org) to keep clean traffic moving at maximum speed.
- Proactive Monitoring: 24/7 edge ruleset updates to neutralize newly discovered CVEs instantaneously.
👉 Ready to protect your site with edge-level security? Upgrade to OneStopWP Managed Hosting today.
See our plans and grab your discount while promotions last.
See plansKeep reading
All posts → WordPress Hosting & OptimizationOneStopWP Optimizer: Free Security Checks and One-Click Fixes for Every OneStopWP Hosted SiteDenny G.Date: Nov 9, 2026
 WordPress Hosting & OptimizationCritical PHP Vulnerabilities (CVE-2026-109618 & CVE-2026-109619): Our Proactive Security ResponseOlivia H.Date: Oct 21, 2026
 General Web HostingWhat Is Bandwidth & What Does Unmetered Bandwidth Really Mean?Olivia H.Date: Jul 24, 2026
Stay up to date
Get WordPress hosting tips, product updates and resources straight to your inbox.